Talare i världsklass
Branschledande experter delar erfarenheter & framtidsspaningar.
Välkommen till Identity Day 2026 och fira 5 år med oss.
För femte året i rad samlas Identity Security-communityn för en heldag fylld av insikter, erfarenhetsutbyte och konkreta perspektiv på hur organisationer stärker kontrollen över identiteter, åtkomst och behörigheter. Identity Day är mötesplatsen där branschkollegor ses, verkliga case delas och samtalen fortsätter långt efter sista sessionen.
I år firar vi 5 år och gör något extra av Identity Day. Posthuset är en viktig del av Identity Day, men i år tänkte vi, varför inte space:a till det lite extra? 2026 tar vi eventet till SPACE 🚀, en helt nyrenoverad lokal i hjärtat av Stockholm, med större scen, bättre flöde och en ännu starkare upplevelse.
Under dagen väntar inspirerande keynotes, panelsamtal och presentationer med fokus på de mest aktuella frågorna inom Identity Security – från strategiska perspektiv till konkreta erfarenheter från organisationer mitt i förändring. I breakout sessions fördjupar vi oss i områden som IGA, PAM, AM och andra centrala delar av en modern identitets- och åtkomststrategi.
Eventet är kostnadsfritt och vi bjuder på god mat och dryck under hela dagen och kvällen. Efter programmet fortsätter vi med mingel och firande fram till kl. 22.
Identity Day är också en möjlighet att nätverka, knyta nya kontakter och dela erfarenheter med andra som arbetar med identitetssäkerhet.
Eventet hålls på svenska, med utvalda presentationer på engelska.
Boka din plats och var med när Identity Day samlar communityn för femte året i rad.


Branschledande experter delar erfarenheter & framtidsspaningar.
Lär dig nya saker och få verktyg att ta med tillbaka till dina kollegor.
Knyt nya kontakter med andra i branschen och bygg ditt nätverk.
Vi ses i nyrenoverade och inspirerande lokaler på SPACE mitt i Stockholm.
Utöver programmet bjuder dagen på extra inslag och upplevelser.
Frukost, fika, lunch och middag med dryck serveras under hela dagen och kvällen.
Eventet är kostnadsfritt för dig som deltar.
Dagen avslutas med middag och mingel fram till kl. 22.00.
Fira fem år av kunskapsdelning och community tillsammans med oss.
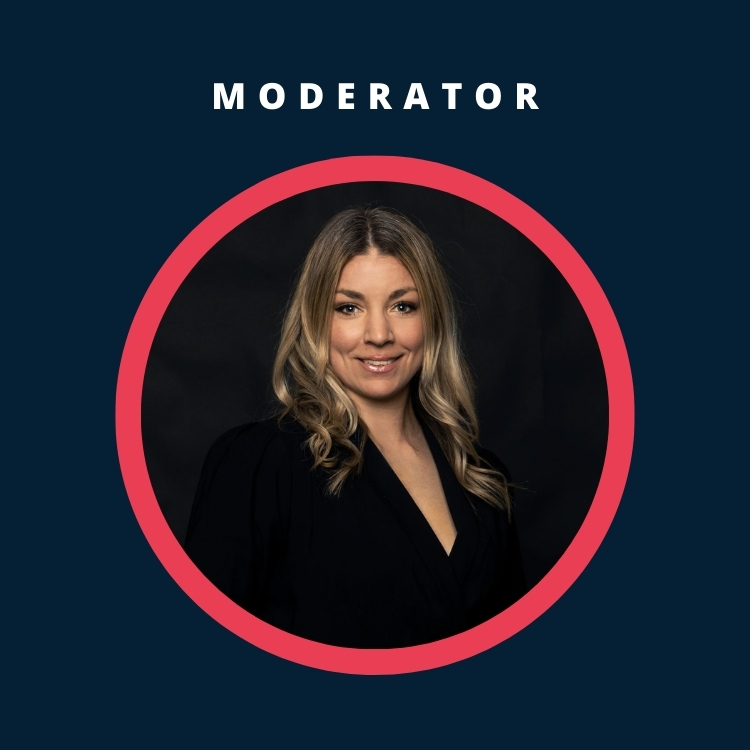
Moderator
Dagen leds av Johanna Samuelson – en erfaren och engagerande konferencier som med skärpa, värme och humor guidar dig genom programmet.
Johanna Samuelson är en erfaren och uppskattad konferencier, programledare och komiker, känd för sin kvicktänkthet, humor och värme. Med en bakgrund inom teater och stand-up har hon en unik förmåga att fånga publiken och skapa en levande atmosfär på scen.
Johanna har tidigare lett evenemang för stora koncerner som DHL, Cygate och LeoVegas, och har även arbetat internationellt. Detta blir hennes fjärde år som konferencier på Identity Day-scenen.

Sales Manager Key Accounts
Vem bestämmer när AI:n börjar agera?
Idag kan AI inte bara skriva texter, utan även fatta beslut och utföra handlingar. Men hur vet vi att det sker på rätt sätt? I den här sessionen visar Yubico hur vi säkerställer mänsklig kontroll i en automatiserad värld. Vi tittar på hur fysisk säkerhetsteknik kan användas för att godkänna viktiga beslut och skapa tydligt ansvar. Lär dig hur vi bygger tillit till AI genom att alltid hålla människan ”i loopen”.
Fredrik Hallberg har över 13 års erfarenhet inom cybersäkerhetsbranschen och har arbetat på organisationer som Thales, Transmit Security och Keypasco, där han framgångsrikt har öppnat nya marknader och lyft fram vikten av stark användarautentisering inom flera olika branscher. Idag är han försäljningschef för Key Accounts med ansvar för Norden och Baltikum på Yubico.
Chief Identity Security Advisor
Runtime, Inline, Real-Time: Securing Identity in the AI-Attack Era
Ending the age-old assumption that defenders have time to respond, frontier AI attacks now compress the kill chain into minutes — chaining misconfigurations at machine speed, without hesitation or fatigue. Detection turns forensic. Patching and access reviews simply can’t keep up.
What stops the attack is access itself, the one checkpoint every identity — human or machine — still has to pass through. Using real-world examples, this session explores why identity is becoming the next control point against AI-powered attacks.
Rob Ainscough is the Chief Identity Security Advisor at Silverfort and a seasoned leader in identity and access management. With over a decade of experience building and scaling IAM programs in complex, global environments, Rob brings deep expertise in access governance, privileged access, and secure credentialing. He is known for simplifying identity security challenges and driving automation and risk reduction at scale.
Principal Solutions Consultant
Cybersäkerhet i AI‑eran
När organisationer går in i AI‑eran har säkerhetsinsatserna aldrig varit mer kritiska. I denna session talar Sören Pettersson hur OpenText Cybersecurity möjliggör säker och skalbar användning av AI genom att förena identitet, dataskydd, applikationssäkerhet och hotdetektion i en Zero‑Trust‑plattform.
Sören Pettersson har över 20 års erfarenhet inom IAM, inklusive Identity Lifecycle, Identity Governance och Zero‑Trust‑arkitekturer.

Director, Product & Solution Marketing
Beyond Agentic AI: Building the Converged Identity Fabric for Every Digital Moment
Agentic AI is here, and it is forcing enterprises to rethink identity at scale. Machine and non-human identities already outnumber human identities by more than 80 to 1, and agentic AI will only accelerate that imbalance as it grows in scope across enterprise ecosystems. But while agentic AI is a paradigm shift, it is not a standalone identity problem. It is the latest use case inside a broader convergence challenge: how to secure every digital moment across customer, employee, partner, third party and agentic AI access journey.
Join Adam Price of Ping Identity for a keynote session exploring why the answer to agentic AI is not another identity silo, but a converged identity fabric.
With over 15 years in B2B technology, I’ve built a career helping organisations navigate growth through purposeful go-to-market (GTM) leadership. My work has always been about connecting people, ideas, and markets across cybersecurity, SaaS, digital identity, and digital innovation. I began my career in policy and performance, progressed through public service and digital innovation, and found my home in driving go-to-market success in biometrics and identity and access management (IAM). I specialise in building and executing GTM strategies that deliver growth and market impact. Across start-ups, scale-ups, post-IPO firms, and global enterprises, I’ve aligned product, marketing, sales, and partner ecosystems to drive new market entry, sales acceleration, and brand leadership.

Blue Team Lead
Worst Case Walkthrough: An Interactive Crisis Simulation
Yvette Muszynski and Lisa Lobmeyer take you on a journey to experience a cyber crisis, showing offensive and defensive elements of what happens when organizations get hacked. Get ready for an interactive session where you influence how the crisis evolves.
Lisa is leading Security Research Labs’ incident response team. She is an experienced DFIR-Specialist, managing and building teams that help organizations affected by cybersecurity incidents while at the same time trying to minimize the impact by advancing organizations’ Cyber Defense capabilities. She aims to build a bridge from technical issues to real world impact, translating for effective decision-making for management.

Offensive Cloud Security Team Lead
Worst Case Walkthrough: An Interactive Crisis Simulation
Yvette Muszynski and Lisa Lobmeyer take you on a journey to experience a cyber crisis, showing offensive and defensive elements of what happens when organizations get hacked. Get ready for an interactive session where you influence how the crisis evolves.
Yvette Muszynski leads the Offensive Cloud Security Team at Security Research Labs, based in Berlin. She is passionate about digging into technology, finding security issues, as well as working on solutions to secure the same. Coming from an electrical engineering background, she applies her cross-domain knowledge to think outside the box when simulating attacks against her clients.

Principal Channel Solutions Engineer
Identity Intelligence Meets Agentic AI
As AI agents become increasingly autonomous, identity is becoming one of the most critical security challenges of the agentic world. This session, presented by Ping Identity, explores how organizations can secure identities across humans, machines, and AI agents as they interact, make decisions, and access resources on behalf of users and businesses. We’ll examine the evolving role of authentication, authorization, delegated access, and trust—and how identity can provide the foundation for secure, accountable, and scalable agentic experiences.
Gagan started his career in IAM with companies like Sun Microsystems and CA Technologies in Australia, then moved to Enterprise Security working in Sales Engineering and Customer roles with F5 Networks and Insurance and Telecommunication companies in Australia. Hen then moved to UK in 2020 with Deloitte Consulting. A global citizen with strong cross-domain functional application experience, its interlocks with bottom-up approach that covers end to end, starting from Infrastructure and Security to functional aspects at the application/solution level, achieving the business outcome is what makes Gagan to be able to operate at all levels of technical, management and commercial aspects with customers.

Senior Solutions Engineer
AI for Identity Security, Identity Security for AI
AI is reshaping identity security in two fundamentally different ways.
On one hand, AI is helping organizations make sense of overwhelming complexity. By identifying patterns, highlighting anomalies, and providing meaningful context, it enables people to make better access decisions with greater confidence instead of getting lost in endless reviews and entitlement data.
On the other hand, AI agents are becoming a new class of enterprise identity. As they begin acting on behalf of people and businesses, identity security provides the framework for discovering them, establishing accountability, managing their access, and ensuring they operate within defined guardrails. Join us as we explore how AI makes identity security smarter and how identity security enables organizations to adopt AI with confidence.
Trey McGlaun is a Senior Solutions Engineer at Saviynt, covering named accounts across the Nordics. He has spent 20+ years in enterprise technology, including founding and exiting an identity services company and several years in Strategic Solutions Engineering across the Nordic identity governance market. Based in Älvkarleby, Sweden, he works with Nordic identity teams on how AI is reshaping the discipline, especially around non-human identities and the governance gap most organizations are only beginning to confront.

Field Strategist
The Digital Identity Control Plane for Agentic AI
Agentic AI, bots and other non‑human identities (NHIs) increasingly act autonomously–often with privileged access. Securing access for these identities requires us to revisit traditional user-centric identity models. In this session we will look at how all elements of Digital Identity security work together to address access governance for these new classes of identity.
Rob specializes in helping organizations integrate Digital Identity into their Cybersecurity strategies. With extensive experience in identity management, Rob has held roles ranging from developer and consultant to technical sales. Before joining One Identity, he worked at Sun Microsystems and Oracle.

Pre-Sales Engineer, EMEA
Providing value through behaviour driven governance
An effective way to right-size what people have access to and gaining value from less risk and threat exposure to potential cost savings.
Ingvar Johansson is an IT professional with more than 35 years in the IT industry. Ingvar has been focusing on Identity and Access Governance for the last 20+ years working for several leading IGA vendors. Ingvar is currently working at One Identity as a Principal Solutions Architect focusing on IAM in the EMEA region. Ingvar’s primary responsibility has always been as a solutions architect in a pre-sale role with the additional responsibility as a technical architect/consultant

Senior Sales Engineer | IAM Evangelist
Dela det som har betydelse. Privacy first!
I dagens digitala landskap är vi vana vid att logga in och omedelbart dela med oss av en stor mängd personlig data – ofta långt mer än vad som krävs. Vår standardmodell är full identifiering. Men måste det vara så? Under den här sessionen utmanar vi konventionen och skiftar fokus. Istället för att fråga ”Vem är du och visa mig allt om dig?”, frågar vi: ”Har du rättigheten att se detta?”. Med ”Privacy first!” som ledstjärna diskuterar vi hur autentisering och tillit kan byggas på vad som faktiskt har betydelse: dina behörigheter och rättigheter, inte din fulla biografi.
With a strong technical foundation and deep expertise in digital identity and access management (IAM), Anders brings a unique blend of engineering acumen and strategic vision to the stage. As a seasoned professional in the IAM space, Anders plays a pivotal role in sales engineering, solution architecture, and defining product requirements—bridging the gap between complex technology and real-world business needs.
A passionate IAM evangelist and prolific blog writer, Anders is dedicated to making digital identity accessible and actionable. Beyond thought leadership, they also create compelling marketing assets including instructional videos, use case guides, solution documents, and step-by-step technical tutorials. Whether driving product innovation or educating the industry, Anders is known for delivering insights with clarity, energy, and impact.

Field CTO
Your Next Identity Risk Isn’t Human – The Governance Gap You Can’t Ignore
Organizations are deploying AI agents into production faster than their governance programs can adapt. These agents access sensitive data, execute workflows, delegate tasks to other agents, and take actions autonomously, all while using service accounts, API credentials, and OAuth tokens that are often themselves ungoverned.
In this session, we break down the governance complexity that AI agents introduce and outline what organizations need to have in place before agent adoption outpaces their ability to maintain security and compliance.
With over 25 years of global experience in cybersecurity and a focus on Identity & Access Management, Paul Walker is a seasoned professional known for his exceptional communication and problem-solving skills. Currently serving as a Field CTO at Omada, he brings a wealth of expertise in value selling, product growth, and IAM solution evangelism. Paul has held key positions at Clear Skye, One Identity, Dell, and Oracle consistently driving technical strategy and maintaining impactful relationships with customers and partners.

Principal Engineer
Access First: Why the Agentic Era Demands a New Security Posture
AI agents and autonomous services are not just replacing human users. They are acting on their behalf, inside your systems, with real permissions and real consequences. This changes the interaction surface between customers, partners and businesses in ways identity alone was never designed to handle. This session makes the case for putting access at the center of your security architecture. Drawing on patterns proven in API-first platforms, we explore how organizations can distinguish agents from humans and move from static permissions to a zero standing privilege posture using intelligent tokens. The approach applies whether you are managing in-house agents or unknown third-party services reaching into your data.
Daniel Lindau is an Identity Specialist and Principal Engineer – Director of Technical Enablement at Curity. He helps organizations design and implement robust identity and API security solutions, drawing on years of experience as both a solution architect and developer. Daniel is an active follower of the OpenID community and regularly shares his insights on topics such as decentralized identity, verifiable credentials, AI security and building secure digital ecosystems at industry events.

Manager, Solution Engineering
Adaptive Identity – Redefining security for an agentic world
The rules of security have fundamentally changed. Static defenses weren’t built for a world of cloud complexity, the rise of AI, dynamic threats, and autonomous change. As identities multiply and risk evolves in real time, security must continuously adapt to keep pace.
This session introduces adaptive identity—a modern approach that transforms identity from a passive, rigid control model into an intelligent, dynamic defense layer. Learn how continuous visibility, real-time risk analysis, and automated governance enable organizations to anticipate threats, enforce the right access at the right time, and respond instantly to change. Discover how adaptive identity strengthens resilience, reduces risk, and empowers your organization to innovate securely in an increasingly dynamic world.
Mikael Wikström works as a Cyber Security Technical Advisor covering the Nordics region where he assists enterprises and organizations in defining the strategy and adoption of an integrated Identity Governance Platform. Mikael has more than 30 years experience in the Cyber Security software industry, where he has lead teams in the development and implementation of complex Cyber Security solutions with a focus on Identity Governance, Identity Management, Access Management in a wide range of organizations and enterprises.

Head of Cybersecurity
One platform, every identity: Schibsted’s blueprint for identity security at scale
With the increasing complexity of operating in a highly dynamic digital media space, Schibsted needed a single, authoritative approach to identity—one that treats service accounts, machine identities, and AI agents with the same rigor as employees. With SailPoint, Schibsted unified visibility and control in one adaptive platform that governs access dynamically as conditions change. This session shows how leading Nordic media company turned fragmented identity data into a strategic security advantage.

Head of Global Channel & Alliances
The Global Identity Debate: Rethinking Customer Identity Across Brands, Borders, and Business Units
Every enterprise operating across multiple brands and markets eventually hits the same fork in the road: how do you get a real picture of the customer when data residency law, regional autonomy, and internal politics all push toward separation? Some organizations answer this by replicating their entire identity stack region by region: a separate instance for every market or compliance zone. Others take the opposite path: keep one resolved identity across every brand and border, and govern the data underneath it, deciding attribute by attribute who owns it, where it lives, and who’s allowed to see it.
Neither answer is automatically right. Each comes with real trade-offs in compliance simplicity, operational overhead, and how well the business actually ends up understanding its own customers.
This session lays out both paths and the trade-offs behind each. Strivacity will be joined by a customer who has lived this decision firsthand, sharing their evaluation process, what they weighed, and where the theory met reality. Built for identity leaders and practitioners facing the same challenges and decisions.

H&M
The Global Identity Debate: Rethinking Customer Identity Across Brands, Borders, and Business Units
Every enterprise operating across multiple brands and markets eventually hits the same fork in the road: how do you get a real picture of the customer when data residency law, regional autonomy, and internal politics all push toward separation? Some organizations answer this by replicating their entire identity stack region by region: a separate instance for every market or compliance zone. Others take the opposite path: keep one resolved identity across every brand and border, and govern the data underneath it, deciding attribute by attribute who owns it, where it lives, and who’s allowed to see it.
Neither answer is automatically right. Each comes with real trade-offs in compliance simplicity, operational overhead, and how well the business actually ends up understanding its own customers.
This session lays out both paths and the trade-offs behind each. Strivacity will be joined by a customer who has lived this decision firsthand, sharing their evaluation process, what they weighed, and where the theory met reality. Built for identity leaders and practitioners facing the same challenges and decisions.
Neeraj Shandilya is an Engineering Manager working in the Customer Identity and Access Management (CIAM) space at H&M. He focuses on building and evolving scalable customer identity platforms supporting large-scale digital ecosystems.
His work includes CIAM architecture, authentication and authorization, identity provider integration, customer identity migration, API design, and integration patterns across web and mobile applications. Neeraj has been closely involved in the integration and implementation of Strivacity as part of H&M’s customer identity platform modernisation, with a focus on building scalable, secure, and flexible identity capabilities.
With a strong software engineering background, Neeraj brings a practical perspective to the intersection of identity architecture, system integration, security, engineering, and customer experience.

Senior Solution Consultant
How to secure your AI/NHI credentials and tokens – from zero visibility to full governance in just days
As cloud environments and automated pipelines expand, machine credentials are proliferating faster than security teams can track them. Storing them in a vault protects credentials at rest, but it doesn’t answer who owns them, where they leak, or what permissions they actually use. In this fast-paced 20-minute session, we bridge the gap between static secrets management and dynamic identity governance. Learn how to rapidly uncover unmanaged tokens, map credential lineage to business owners, and enforce automated lifecycle guardrails – achieving complete non-human visibility and control in days without disrupting developer velocity.
Starta dagen med en god frukost och värdefullt nätverkande.

Vår briljanta moderator Johanna inleder dagen.

The rules of security have fundamentally changed. Static defenses weren’t built for a world of cloud complexity, the rise of AI, dynamic threats, and autonomous change. As identities multiply and risk evolves in real time, security must continuously adapt to keep pace.
This session introduces adaptive identity—a modern approach that transforms identity from a passive, rigid control model into an intelligent, dynamic defense layer. Learn how continuous visibility, real-time risk analysis, and automated governance enable organizations to anticipate threats, enforce the right access at the right time, and respond instantly to change. Discover how adaptive identity strengthens resilience, reduces risk, and empowers your organization to innovate securely in an increasingly dynamic world.

Agentic AI, bots and other non‑human identities (NHIs) increasingly act autonomously-often with privileged access. Securing access for these identities requires us to revisit traditional user-centric identity models. In this session we will look at how all elements of Digital Identity security work together to address access governance for these new classes of identity.

Agentic AI is here, and it is forcing enterprises to rethink identity at scale. Machine and non-human identities already outnumber human identities by more than 80 to 1, and agentic AI will only accelerate that imbalance as it grows in scope across enterprise ecosystems. But while agentic AI is a paradigm shift, it is not a standalone identity problem. It is the latest use case inside a broader convergence challenge: how to secure every digital moment across customer, employee, partner, third party and agentic AI access journey.
Join Adam Price of Ping Identity for a keynote session exploring why the answer to agentic AI is not another identity silo, but a converged identity fabric.
Njut av en välsmakande fika, sponsrad av våra härliga sponsorer: Opentext, Saviynt, Yubico och Fortified ID

Yvette Muszynski and Lisa Lobmeyer take you on a journey to experience a cyber crisis, showing offensive and defensive elements of what happens when organizations get hacked. Get ready for an interactive session where you influence how the crisis evolves.

I dagens digitala landskap är vi vana vid att logga in och omedelbart dela med oss av en stor mängd personlig data – ofta långt mer än vad som krävs. Vår standardmodell är full identifiering. Men måste det vara så? Under den här sessionen utmanar vi konventionen och skiftar fokus. Istället för att fråga "Vem är du och visa mig allt om dig?", frågar vi: "Har du rättigheten att se detta?". Med "Privacy first!" som ledstjärna diskuterar vi hur autentisering och tillit kan byggas på vad som faktiskt har betydelse: dina behörigheter och rättigheter, inte din fulla biografi.

När organisationer går in i AI‑eran har säkerhetsinsatserna aldrig varit mer kritiska. I denna session talar Sören Pettersson hur OpenText Cybersecurity möjliggör säker och skalbar användning av AI genom att förena identitet, dataskydd, applikationssäkerhet och hotdetektion i en Zero‑Trust‑plattform.

With the increasing complexity of operating in a highly dynamic digital media space, Schibsted needed a single, authoritative approach to identity—one that treats service accounts, machine identities, and AI agents with the same rigor as employees. With SailPoint, Schibsted unified visibility and control in one adaptive platform that governs access dynamically as conditions change. This session shows how leading Nordic media company turned fragmented identity data into a strategic security advantage.

An effective way to right-size what people have access to and gaining value from less risk and threat exposure to potential cost savings.

Idag kan AI inte bara skriva texter, utan även fatta beslut och utföra handlingar. Men hur vet vi att det sker på rätt sätt? I den här sessionen visar Yubico hur vi säkerställer mänsklig kontroll i en automatiserad värld. Vi tittar på hur fysisk säkerhetsteknik kan användas för att godkänna viktiga beslut och skapa tydligt ansvar. Lär dig hur vi bygger tillit till AI genom att alltid hålla människan ”i loopen”.
Vi bjuder på en välsmakande lunch sponsrad av Silverfort och Omada. Passa på att nätverka med branschkollegor och hälsa på våra sponsorer i deras montrar.

As cloud environments and automated pipelines expand, machine credentials are proliferating faster than security teams can track them. Storing them in a vault protects credentials at rest, but it doesn't answer who owns them, where they leak, or what permissions they actually use. In this fast-paced 20-minute session, we bridge the gap between static secrets management and dynamic identity governance. Learn how to rapidly uncover unmanaged tokens, map credential lineage to business owners, and enforce automated lifecycle guardrails - achieving complete non-human visibility and control in days without disrupting developer velocity.

As AI agents become increasingly autonomous, identity is becoming one of the most critical security challenges of the agentic world. This session, presented by Ping Identity, explores how organizations can secure identities across humans, machines, and AI agents as they interact, make decisions, and access resources on behalf of users and businesses. We’ll examine the evolving role of authentication, authorization, delegated access, and trust—and how identity can provide the foundation for secure, accountable, and scalable agentic experiences.

AI is reshaping identity security in two fundamentally different ways.
On one hand, AI is helping organizations make sense of overwhelming complexity. By identifying patterns, highlighting anomalies, and providing meaningful context, it enables people to make better access decisions with greater confidence instead of getting lost in endless reviews and entitlement data.
On the other hand, AI agents are becoming a new class of enterprise identity. As they begin acting on behalf of people and businesses, identity security provides the framework for discovering them, establishing accountability, managing their access, and ensuring they operate within defined guardrails. Join us as we explore how AI makes identity security smarter and how identity security enables organizations to adopt AI with confidence.
Dagens breakout sessions är nu avslutade och programmet fortsätter på main stage SPACE Arena.

Ending the age-old assumption that defenders have time to respond, frontier AI attacks now compress the kill chain into minutes — chaining misconfigurations at machine speed, without hesitation or fatigue. Detection turns forensic. Patching and access reviews simply can't keep up.
What stops the attack is access itself, the one checkpoint every identity — human or machine — still has to pass through. Using real-world examples, this session explores why identity is becoming the next control point against AI-powered attacks.

Organizations are deploying AI agents into production faster than their governance programs can adapt. These agents access sensitive data, execute workflows, delegate tasks to other agents, and take actions autonomously, all while using service accounts, API credentials, and OAuth tokens that are often themselves ungoverned.
In this session, we break down the governance complexity that AI agents introduce and outline what organizations need to have in place before agent adoption outpaces their ability to maintain security and compliance.
Njut av en välsmakande fika, sponsrad av våra härliga sponsorer: Opentext, Saviynt, Yubico och Fortified ID

AI agents and autonomous services are not just replacing human users. They are acting on their behalf, inside your systems, with real permissions and real consequences. This changes the interaction surface between customers, partners and businesses in ways identity alone was never designed to handle. This session makes the case for putting access at the center of your security architecture. Drawing on patterns proven in API-first platforms, we explore how organizations can distinguish agents from humans and move from static permissions to a zero standing privilege posture using intelligent tokens. The approach applies whether you are managing in-house agents or unknown third-party services reaching into your data.

Every enterprise operating across multiple brands and markets eventually hits the same fork in the road: how do you get a real picture of the customer when data residency law, regional autonomy, and internal politics all push toward separation? Some organizations answer this by replicating their entire identity stack region by region: a separate instance for every market or compliance zone. Others take the opposite path: keep one resolved identity across every brand and border, and govern the data underneath it, deciding attribute by attribute who owns it, where it lives, and who's allowed to see it. Neither answer is automatically right. Each comes with real trade-offs in compliance simplicity, operational overhead, and how well the business actually ends up understanding its own customers. This session lays out both paths and the trade-offs behind each. Strivacity will be joined by a customer who has lived this decision firsthand, sharing their evaluation process, what they weighed, and where the theory met reality. Built for identity leaders and practitioners facing the same challenges and decisions.
Ta en välbehövlig bensträckare, fyll på kaffekoppen och passa på att mingla med våra sponsorer under pausen.
Panel discussion with our experts from SailPoint, One Identity, Ping Identity, Silverfort, Omada, and Curity.

Följ med oss in i kvällen - börja med ett glas bubbel och njut av en härlig middag. Kvällen sponsras av SailPoint, One Identity och Ping Identity.







Arctic Group är din strategiska partner för att ta nästa steg mot ökad säkerhet. Vi hjälper er att stärka er digitala infrastruktur och skydda er verksamhet mot framtidens utmaningar. Med vår expertis inom cybersäkerhet och digitalisering ser vi till att ni kan möta nya utmaningar med trygghet och innovation. Tillsammans bygger vi en hållbar och säker digital framtid för er.
Vi på ID North är specialiserade inom identitetssäkerhet och hjälper ditt företag att skydda och hantera era digitala identiteter. Med oss får du tillgång till branschens främsta experter och den senaste tekniken. Våra lösningar säkerställer effektivitet, smidiga processer, omfattande kontroll och skydd på högsta nivå. Tillsammans skapar vi en stabil grund för tillit, innovation och framgång. Säkra din organisations framtid med oss.
Ja! Även om eventet är kostnadsfritt, vill vi gärna påminna om att det krävs en föranmälan för att delta. Vi ser verkligen fram emot att välkomna er och vill säkerställa att alla får en fantastisk upplevelse!
Nej! Då det är ett kostnadsfritt event har vi begränsat antal platser. Vi kommer inte kunna ta emot anmälningar på plats vid eventet, så säkra din plats redan idag!
Eventet är till för alla företag / organisationer som verkar i digitala miljöer. Arbetar ni med hybrida arbetsplatser? Har du en digital profil? Hanterar ni personliga uppgifter? Då är identitetssäkerhet av högsta relevans.
Självklart, se bara till att anmäla er så rätt mängd mat och platser finns. Bjud med en vän eller en kollega och anmäl er idag.
Nätverk, mat & mingel. På plats under dagen och kvällen kommer du även ha möjlighet att knyta kontakter inom branschen, underhållas och äta gott.
Eventet är på svenska med inslag av presentationer som hålls på engelska.
SPACE
Sergelgatan 2
111 57 Stockholm
SPACE ligger mitt i centrala Stockholm. Lokalen är toppmodern och erbjuder en inspirerande miljö för större event och möten. Hit tar du dig enkelt via T-Centralen och Stockholms Centralstation, bara några minuters promenad bort, med anslutningar till tunnelbana, pendeltåg, buss och fjärrtåg.


